thinQmaster — Security+
CompTIA · SY0-701 · Associate
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
417 multiple choice · 83 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CCNA
Cisco · 200-301 · Associate
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
389 multiple choice · 63 choose two · 25 drag and drop · 23 put in order
Domains, and how many questions each
- Network Infrastructure and Connectivity100
- Switching and Network Access100
- IP Routing100
- Network Services and Security100
- AI and Network Operations and Management100
A real exam experience
- Timed simulation — 60 questions in 120 minutes, weighted to the blueprint, no feedback until the end.
- 5 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CISSP
ISC2 · Flagship
825 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
825 multiple choice
Domains, and how many questions each
- Security and Risk Management35
- Asset Security103
- Security Architecture and Engineering238
- Communication and Network Security216
- Identity and Access Management122
- Security Assessment and Testing24
- Security Operations44
- Software Development Security43
A real exam experience
- Timed simulation — 125 questions in 240 minutes, weighted to the blueprint, no feedback until the end.
- 8 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — Network+
CompTIA · N10-009 · Associate
115 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
101 multiple choice · 14 choose two
Domains, and how many questions each
- 1.0 Networking Concepts115
- 2.0 Network Implementation0
- 3.0 Network Operations0
- 4.0 Network Security0
- 5.0 Network Troubleshooting0
A real exam experience
- Timed simulation — 90 questions in 90 minutes, weighted to the blueprint, no feedback until the end.
- 5 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — A+ Core 1
CompTIA · 220-1201 · Associate
1,000 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
816 multiple choice · 184 choose two
Domains, and how many questions each
- Mobile Devices130
- Networking230
- Hardware250
- Virtualization and Cloud Computing110
- Hardware and Network Troubleshooting280
A real exam experience
- Timed simulation — 90 questions in 90 minutes, weighted to the blueprint, no feedback until the end.
- 5 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — A+ Core 2
CompTIA · 220-1202 · Associate
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
400 multiple choice · 100 choose two
Domains, and how many questions each
- Operating Systems140
- Security140
- Software Troubleshooting115
- Operational Procedures105
A real exam experience
- Timed simulation — 90 questions in 90 minutes, weighted to the blueprint, no feedback until the end.
- 4 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CCNP ENCOR
Cisco · 350-401 · Professional
thinQmaster — AutoOps+
CompTIA · AT0-001 · Professional
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
400 multiple choice · 100 choose two
Domains, and how many questions each
- Automation Coding Concepts155
- System Configuration125
- Continuous Integration120
- Continuous Delivery100
A real exam experience
- Timed simulation — 60 questions in 60 minutes, weighted to the blueprint, no feedback until the end.
- 4 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CloudNetX
CompTIA · CNX-001 · Flagship
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
375 multiple choice · 125 choose two
Domains, and how many questions each
- Network Architecture Design155
- Network Security140
- Operations, Monitoring and Performance80
- Network Troubleshooting125
A real exam experience
- Timed simulation — 90 questions in 165 minutes, weighted to the blueprint, no feedback until the end.
- 4 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — DataAI
CompTIA · DY0-001 · Flagship
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
375 multiple choice · 125 choose two
Domains, and how many questions each
- Mathematics and Statistics85
- Modeling, Analysis and Outcomes120
- Machine Learning120
- Operations and Processes110
- Specialized Applications of Data Science65
A real exam experience
- Timed simulation — 90 questions in 165 minutes, weighted to the blueprint, no feedback until the end.
- 5 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — Tech+
CompTIA · FC0-U71 · Foundational
300 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
262 multiple choice · 38 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CySA+
CompTIA · CS0-003 · Professional
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
400 multiple choice · 100 choose two
Domains, and how many questions each
- Security Operations165
- Vulnerability Management150
- Incident Response and Management100
- Reporting and Communication85
A real exam experience
- Timed simulation — 85 questions in 165 minutes, weighted to the blueprint, no feedback until the end.
- 4 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — PenTest+
CompTIA · PT0-003 · Professional
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
421 multiple choice · 79 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — Project+
CompTIA · PK0-005 · Associate
300 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
253 multiple choice · 47 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
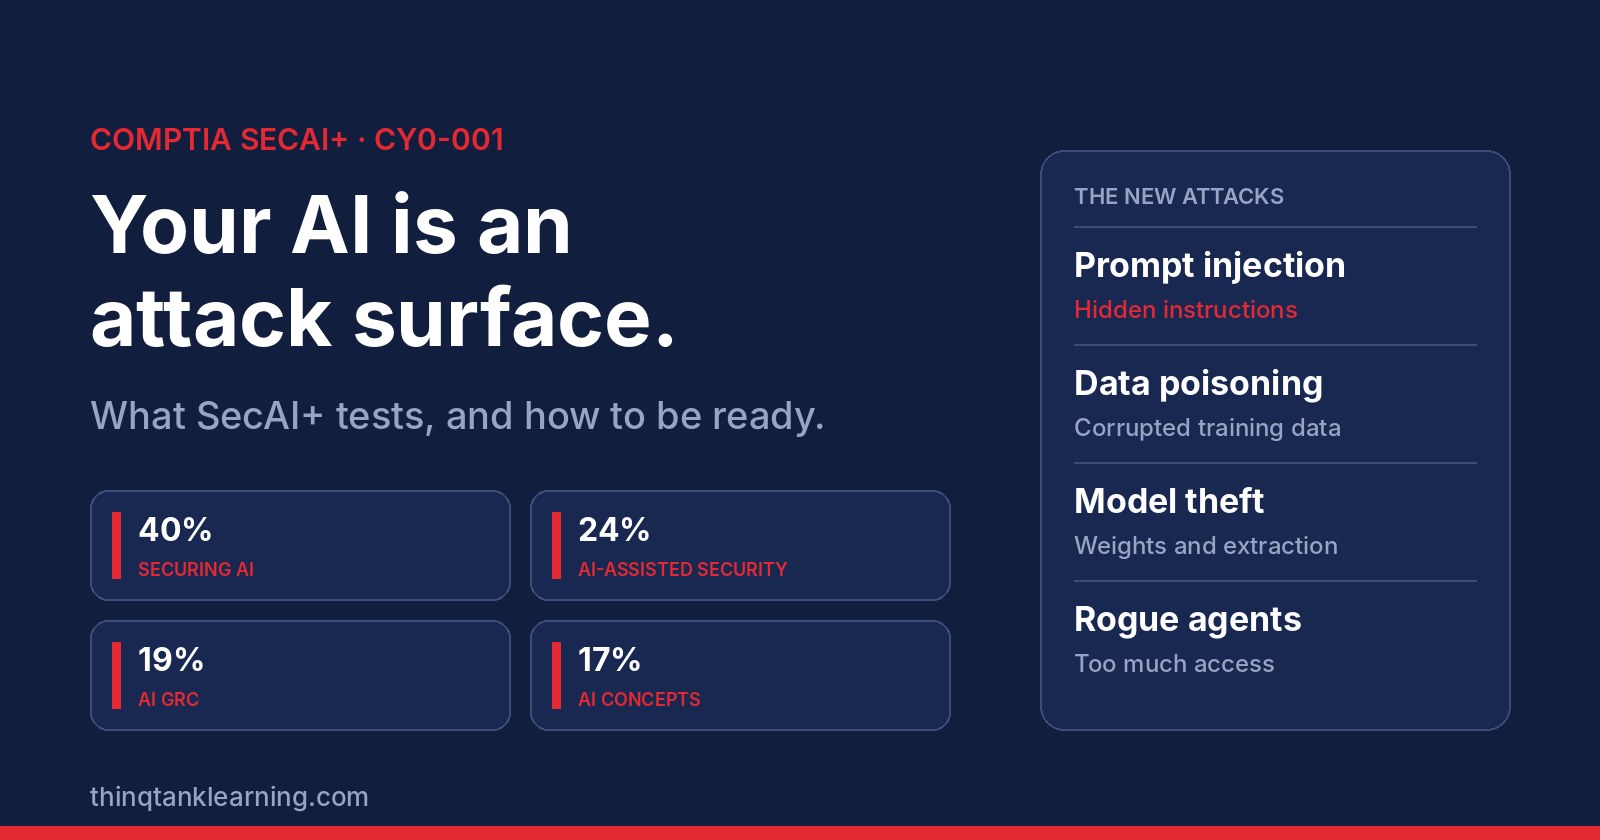
thinQmaster — SecAI+
CompTIA · CY0-001 · Professional
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
414 multiple choice · 86 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — SecurityX (CASP+)
CompTIA · CAS-005 · Flagship
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
414 multiple choice · 86 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — Linux+
CompTIA · XK0-006 · Associate
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
400 multiple choice · 100 choose two
Domains, and how many questions each
- System Management115
- Security105
- Scripting, Containers and Automation95
- Troubleshooting185
A real exam experience
- Timed simulation — 90 questions in 90 minutes, weighted to the blueprint, no feedback until the end.
- 4 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — Data+
CompTIA · DA0-002 · Associate
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
400 multiple choice · 100 choose two
Domains, and how many questions each
- Data Concepts and Environments100
- Data Acquisition and Preparation110
- Data Analysis120
- Visualization and Reporting100
- Data Governance70
A real exam experience
- Timed simulation — 90 questions in 90 minutes, weighted to the blueprint, no feedback until the end.
- 5 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — DataSys+
CompTIA · DS0-001 · Associate
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
400 multiple choice · 100 choose two
Domains, and how many questions each
- Database Fundamentals120
- Database Deployment80
- Database Management and Maintenance125
- Data and Database Security115
- Business Continuity60
A real exam experience
- Timed simulation — 90 questions in 90 minutes, weighted to the blueprint, no feedback until the end.
- 5 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — Cloud+
CompTIA · CV0-004 · Associate
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
400 multiple choice · 100 choose two
Domains, and how many questions each
- Cloud Architecture115
- Deployment95
- Operations85
- Security95
- DevOps Fundamentals50
- Troubleshooting60
A real exam experience
- Timed simulation — 90 questions in 90 minutes, weighted to the blueprint, no feedback until the end.
- 6 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — Server+
CompTIA · SK0-005 · Associate
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
415 multiple choice · 85 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CCT Field Technician
Cisco · 800-150 FLDTEC · Associate
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
416 multiple choice · 84 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CCST Networking
Cisco · 100-150 · Foundational
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
418 multiple choice · 82 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CCST Cybersecurity
Cisco · 100-160 · Foundational
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
416 multiple choice · 84 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CCNA Automation
Cisco · 200-901 · Associate
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
415 multiple choice · 85 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CCNA Cybersecurity
Cisco · 200-201 · Associate
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
415 multiple choice · 85 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CCNP ENARSI
Cisco · 300-410 · Professional
thinQmaster — CCNP ENSLD
Cisco · 300-420 · Professional
270 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
172 multiple choice · 53 choose two · 28 drag and drop · 17 put in order
Domains, and how many questions each
- Advanced Addressing and Routing Solutions60
- Advanced Enterprise Campus Networks60
- WAN for Enterprise Networks50
- Network Services50
- Automation50
A real exam experience
- Timed simulation — 55 questions in 90 minutes, weighted to the blueprint, no feedback until the end.
- 5 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CyberOps Professional
Cisco · 350-201 · Professional
thinQmaster — CCNP Security SCOR
Cisco · 350-701 · Professional
thinQmaster — Azure Fundamentals
Microsoft · AZ-900 · Foundational
thinQmaster — Azure Data Fundamentals
Microsoft · DP-900 · Foundational
thinQmaster — Azure AI Fundamentals
Microsoft · AI-900 · Foundational
thinQmaster — Azure Administrator
Microsoft · AZ-104 · Associate
thinQmaster — Azure Network Engineer
Microsoft · AZ-700 · Associate
thinQmaster — Azure Database Administrator
Microsoft · DP-300 · Associate
thinQmaster — Power BI Data Analyst
Microsoft · PL-300 · Associate
thinQmaster — Azure Solutions Architect
Microsoft · AZ-305 · Professional
thinQmaster — CCSP
ISC2 · Professional
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
416 multiple choice · 84 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CGRC
ISC2 · Professional
thinQmaster — CSSLP
ISC2 · Professional
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
416 multiple choice · 84 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — SSCP
ISC2 · Associate
thinQmaster — CISA
ISACA · Professional
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
417 multiple choice · 83 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CISM
ISACA · Professional
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
416 multiple choice · 84 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — CRISC
ISACA · Professional
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
413 multiple choice · 87 choose two
A real exam experience
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.
thinQmaster — C|EH v13
EC-Council · 312-50 · Professional
thinQmaster — C|HFI v11
EC-Council · 312-49 · Professional
thinQmaster — E|CIH v3
EC-Council · 212-89 · Associate
thinQmaster — Cloud Security Essentials
EC-Council · 112-54 · Foundational
thinQmaster — Cloud Practitioner
AWS · Foundational
thinQmaster — GSEC
GIAC · Professional
thinQmaster — JNCIA-Junos
Juniper · Foundational
thinQmaster — PMP
PMI · Professional
thinQmaster — CTS
AVIXA · Associate
500 questions · what is in it
Built like the exam, not like a flashcard deck. The same question shapes you meet on test day, sat against the published blueprint, with a timed paper at full length.
Question types
500 multiple choice
Domains, and how many questions each
- Creating AV Solutions175
- Implementing AV Solutions150
- Supporting AV System Operation75
- Servicing AV Solutions100
A real exam experience
- Timed simulation — 115 questions in 150 minutes, weighted to the blueprint, no feedback until the end.
- 4 domain drills — work one weak area at a time.
- Exhibits — real command output and topology diagrams to read, the way the exam asks them.
- It adapts — miss a domain and the next questions lean that way; master one and it eases off.
- Every answer explained — why the right one is right, and why each wrong one is wrong.